Audited, attested, and current
The paperwork your security team asks for, maintained as a program, not a one-off.
ISO/IEC 27001 certified
information security management
SOC 2 Type 2 completed
controls over time, audited
GDPR compliant
consent, access, and erasure
Candidate data, handled like it matters
The controls below are part of the platform for every customer, not an enterprise add-on.
Tenant isolation
Every customer runs in a logically isolated tenant. Your candidate data is never mixed with, or visible to, another organization.
Consent-gated engagement
Candidates hear clear AI disclosure and give consent before any automated conversation. No consent, no engagement.
Personal-data stripping
Identifying personal data is stripped before AI processing, so models work on qualifications and criteria, not on who someone is.
Deletion & residency
Configurable data residency per tenant, retention windows you set, and deletion workflows that honor erasure requests.
AI runs the work. People make the calls.
The same doctrine holds across the whole platform, from sourcing to offer.
No automated candidate decisions
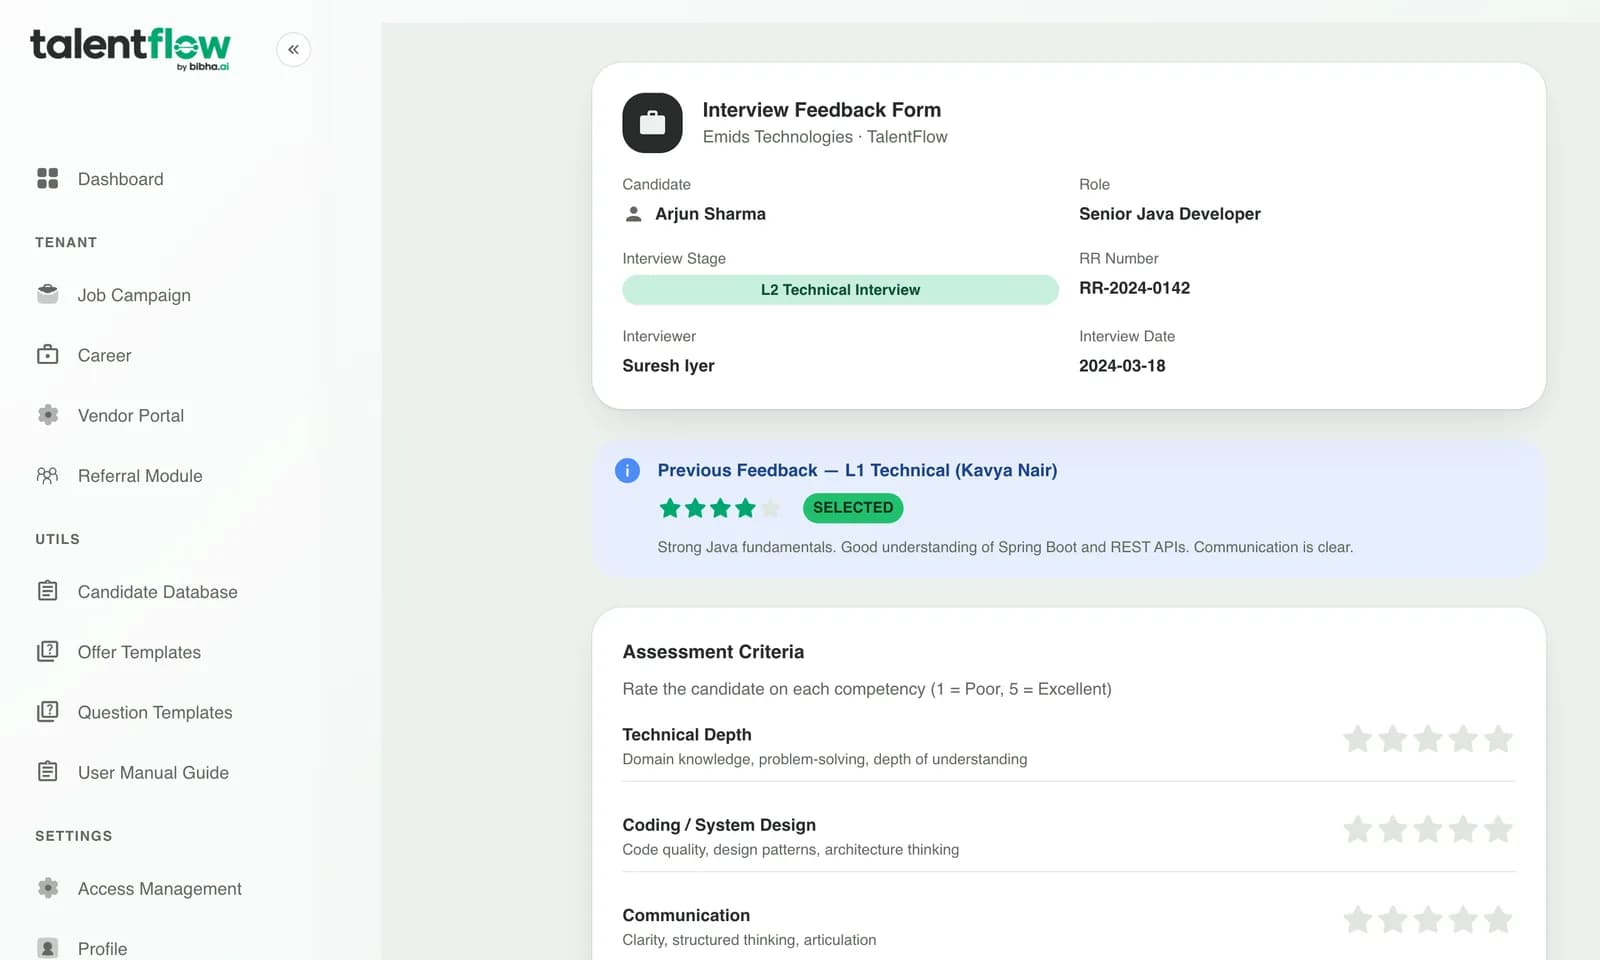
TalentFlow never scores, ranks, recommends, or auto-rejects a candidate.
Human gates at every stage
Shortlists, rejections, and offers are made by recruiters, inside the pipeline.
Deterministic criteria
Screening applies the criteria your team defines, the same way, every time.
See how deterministic screening works
A short list, kept current
TalentFlow runs on a small set of subprocessors covering cloud hosting, email and message delivery, and telephony. The current list, along with security documentation, penetration test summaries, and data processing terms, is maintained in our Trust Center. Data residency is configurable per tenant, and regional requirements are reviewed with your team during onboarding.
Visit the Trust Center