Controls your security team will ask about
Enterprise recruitment software with the governance layer built in, not bolted on: access, structure, auditability, and isolation.
Roles and permissions
Granular access for recruiters, hiring managers, interviewers, and admins, scoped to departments, locations, and entities.
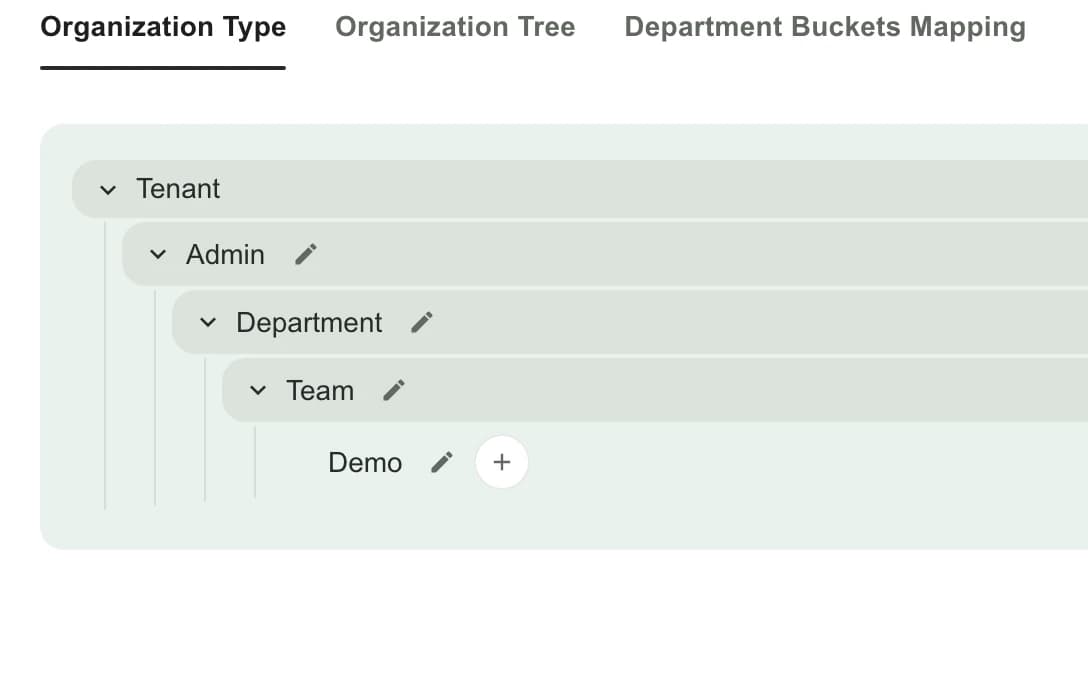
Org hierarchy
Mirror your structure: regions, entities, departments, and teams. Pipelines, permissions, and reporting all respect it.
Audit trails
Every meaningful action is logged with actor and timestamp, so access and changes stay reviewable by your security team.
Tenant isolation
Your data is isolated at the tenant level. It is never shared across customers, and it stays yours, exports included.
Data residency
Choose the region your candidate data lives in, so residency and sovereignty requirements are met by configuration, not by exception.
SSO
Single sign-on with your identity provider, so platform access follows your existing joiner, mover, and leaver process.
Two ways to deploy
Replace the stack or run next to it. Either way, your recruiters work in one pipeline and your system of record stays clean.
Standalone
TalentFlow as your full ATS and system of record.
Requisitions, pipeline, interviews, offers, and analytics in one place
Structured migration from your legacy ATS, supported end to end
One pipeline for every team, region, and entity
Middleware
TalentFlow alongside the ATS you already run.
Powers engagement, interviews, and analytics on top of your current system
Syncs candidates and stages back through verified integrations and webhooks
Prove value with one team before any migration decision
Audited controls, on by default
Consent-gated engagement, human decision gates, and configurable residency come standard on every enterprise plan.
- ISO/IEC 27001 certified
- SOC 2 Type 2 completed
- GDPR compliant
Enterprise platform, answered
Two. Standalone, where TalentFlow is your full ATS and system of record, and middleware, where it runs alongside your existing ATS and powers engagement, interviews, and analytics while syncing back to your system of record.
Each customer runs in an isolated tenant. Data is never shared across customers, access is enforced at the tenant boundary, and you choose the residency region for your candidate data.
TalentFlow is ISO/IEC 27001 certified, SOC 2 Type 2 completed, and GDPR compliant. Evidence and audit reports are available to enterprise buyers during security review.
Yes. Single sign-on works with the major identity providers, so account creation and removal follow your existing identity lifecycle instead of a separate user list.
Permissions are role-based and scoped to the org hierarchy: a recruiter in one region sees their region, a global admin sees everything, and every action lands in the audit trail.
People do. The platform accelerates execution and keeps records clean, but it never scores, ranks, or rejects candidates. Recruiters and hiring managers make every decision.